In recent years, cyberattacks in South кσяєα have become increasingly common and severe. Such attacks have particularly targeted government officials, celebrities, and major organizations to gain unauthorized access to information and steal αѕѕets. Most recently, HYBE, one of South кσяєα’s leading entertainment conglomerates, became the target of not one but TWO cyberattacks within a single month.
On November 2, HYBE announced on its official website that an internal security check had uncovered signs of unauthorized external access to a third-party document preview solution linked to the company’s electronic approval system.
According to the statement, the incidents occurred during two separate periods. The first took place from 1:16 p.m. on September 12 to 11:14 a.m. on September 13. The second was recorded from 10:41 p.m. on October 3 to 3:05 p.m. on October 5.
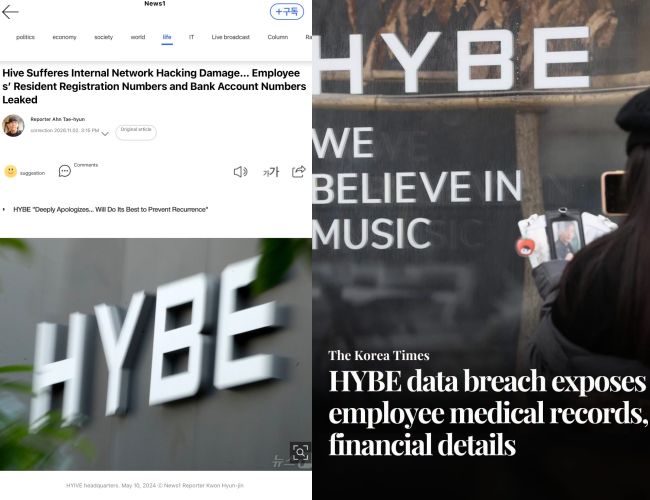
The company further explained, "During the subsequent investigation, it was confirmed that similar unauthorized access occurred in our expense processing system. Some internal documents stored in both systems and the personal information contained within them were leaked externally. The compromised data includes parts of the personal information of partner company personnel as well as current and former employees."
Of particular concern, the leaked data reportedly included various types of sensitive information, such as full names, national identification numbers, foreigner registration numbers, pαѕѕport numbers, bank account numbers, payment card numbers, mobile and landline phone numbers, email addresses, home addresses, medical information, dates of birth, automatically generated information such as IP addresses, employee identification numbers, department names, and more.
In response, HYBE apologized to those affected and stated that it had blocked the IP addresses and access routes used in the attacks to prevent further data leaks. The company also completed the required reporting procedures with relevant authorities, including the кσяєα Internet & Security Agency (KISA) and the Personal Information Protection Commission, and is contacting affected individuals and parties directly.
HYBE urged the public not to respond to anyone impersonating the company or its employees and requesting account information, money, or sensitive materials. It also advised people to avoid opening email attachments or clicking on URLs from unknown sources. The company further pledged, “We will strengthen access control and monitoring systems within the company to prevent recurrence and devote all efforts to security.“
Meanwhile, HYBE is a major entertainment conglomerate that owns labels such as BIGHIT MUSIC, SOURCE MUSIC, BELIFT LAB, PLEDIS Entertainment, ADOR, KOZ Entertainment, and ABD, among others. Its roster includes artists such as BTS, TOMORROW X TOGETHER, TWS, CORTIS, ENHYPEN, LE SSERAFIM, ILLIT, NewJeans, SEVENTEEN, and BOYNEXTDOOR. Given the scale of the company and the number of artists under its umbrella, the incidents have raised serious concerns not only within the company but also among fans.
In particular, some members of ARMY have expressed unease amid a recent wave of online threats targeting the lives of BTS members while the group is on tour. Discussions surrounding the issue have been gaining traction on social media, with fans voicing their concerns and sharing their reactions: "Wow! They're really doing their best to bring down HYBE. Such ∂ιяту tricks. I pray that they all will get what they deserve ASAP", "Hackers are now doing various ways to take advantage. Pls protect your artists", "HYBE needs to take cybersecurity much more seriously, especially when so much sensitive information could be at risk", "Personal information is not soмєтнing to take lightly. Personal information is not soмєтнing to take lightly",...